Etusivu » Access Management

Access Management

Access management acts as a gatekeeper for devices and information systems, allowing users to access systems easily and securely. Access management also protects systems from unauthorized and inappropriate use and monitors their usage.

Access management first ensures that the user is who they claim to be. This is implemented through user authentication, which must always be sufficiently strong for the situation. After that, access management allows the user into the services for which they have been granted rights in identity management.

Systems are used securely when they are easy to use

Secure access management is made effortless and fast for users through, for example, organization-level card and single sign-on, which works on all terminal devices. The user authenticates to the device using, for example, a smart card, after which they have access to applications according to their authorizations without a separate login.

Ask an expert for more information

Authentication and logging into systems must be effortless and fast for users

There are authentication and strong authentication methods for many different needs

Authentication confirms the user’s identity to the system. Authentication can traditionally be done with a username and password, but there is often a need to favor stronger methods for data protection and security.

Authentication can be done in several ways:

  • By knowledge (something you know)
  • By possession (something you have)
  • By biometrics (something you are)

Strong authentication uses more than one method, and in such cases, it is referred to as two-factor or multi-factor authentication.

If authenticating to a device and logging into applications are difficult and slow, it is human nature to develop shortcuts and workarounds, such as shared credentials and sticky notes next to the computer, which weaken security. Usability guides usage in the right direction.  

Strong PKI Authentication Facial Recognition

Organization-level single sign-on is an easy, fast, and secure way to log into systems

Organization-level single sign-on improves system usability by allowing users to access applications with a single authentication, removes the pain of password management, improves security by minimizing the use of weak passwords, and lowers IT support costs by reducing password reset requests. Single sign-on also improves the user experience, increases productivity, and helps ensure a secure way of working.

Shared workstations and mobile devices bring workflow efficiency and cost savings

Shared workstations and mobile devices are common in many industries, such as manufacturing, healthcare, logistics, and retail. As shared resources, they improve efficiency and lower costs, but they also bring significant cybersecurity risks. The security of shared workstations is important for protecting sensitive data, maintaining operational reliability, and complying with statutory requirements.

Organization-level single sign-on secures and streamlines the use of shared workstations and mobile devices, while bringing significant cost savings.

Single Sign-On Shared Devices Shared Mobile Devices

Centralized lifecycle management of all different authentication tools brings benefits

Unified management of credentials and identifiers—including registration, activation, renewal, blocking, and revocation—and policies concerning identifiers.

Read more

Discover how…

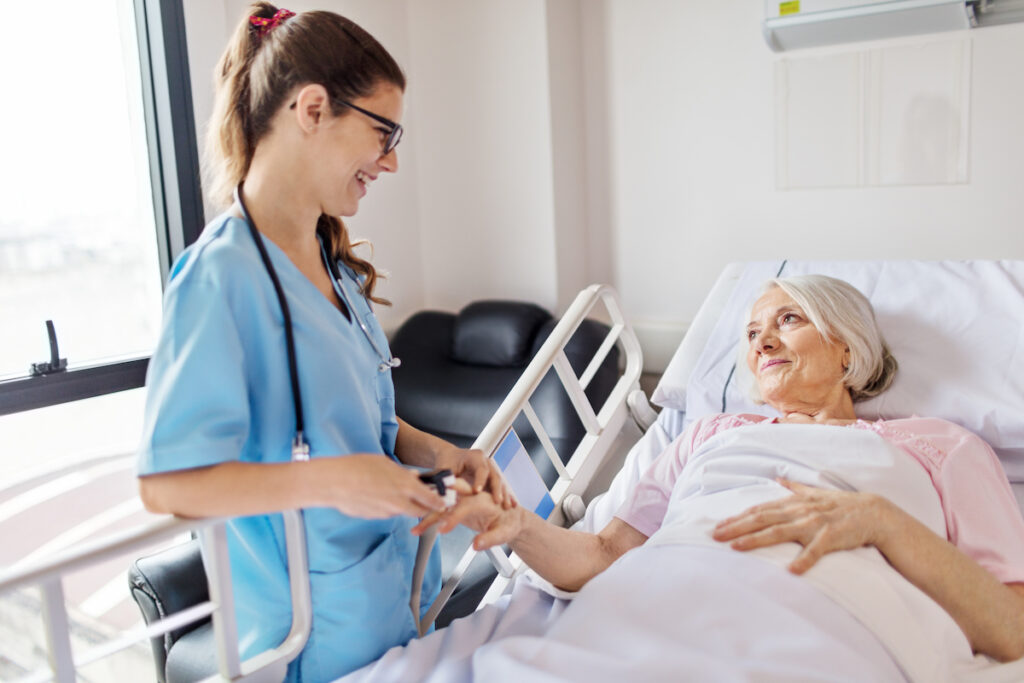
Card and single sign-on in healthcare provides thirty minutes more working time per shift

User studies in healthcare organizations have shown that smart card and single sign-on free up 15–40 minutes more time for patient work per shift for nursing professionals.

In addition, studies show that job satisfaction improves significantly when logging into information systems becomes easier and focus can be placed on patients instead of information technology.

Read more

FIDO2 – secure authentication without passwords and excellent technology for protecting against phishing

FIDO2 is a modern authentication standard that enables secure login without passwords. It utilizes, for example, passkey technology, biometric identifiers, and security keys, effectively protecting users from phishing and credential misuse. CSIT Finland utilizes FIDO2 technology in Imprivata and Pointsharp solutions, which offer organizations secure, user-friendly authentication that supports Zero Trust principles for workstations, applications, and cloud services.

The FIDO2 standard was developed by the FIDO Alliance and W3C, and it is specifically designed to eliminate the need for passwords and make logins phishing-resistant.

Read more

Large encrypted files are transferred in compliance with requirements

The need to send large, sensitive, or even secret files and documents both within and outside the organization is more important than ever.

Our solution integrates directly into the organization’s email client, making email classification, encrypted file transfers, and secure messaging an easy and natural part of sending email. It also removes file size limits, which further improves usability and reduces the load on the email server.

Read more Download brochure

Certificate lifecycle management is undergoing a major transformation – digital trust is the critical infrastructure of the next decade

Certificate Lifecycle Management (CLM) refers to the processes and tools with which an organization manages the entire lifecycle of digital certificates securely and automatically.

Digital trust is built on invisible but critical components. One of the most important is the SSL/TLS certificate, which enables secure web communication, identifies services, and protects data transfer. The importance of certificates is constantly growing. At the same time, their management causes an increasing administrative burden for security teams. Key industry players have made a policy to gradually shorten the maximum validity period of public SSL/TLS certificates to 47 days. For organizations, this means one thing: certificate management is no longer an occasional maintenance task—it is a continuous business-critical process that requires the use of tools for management.

Explore the European solution

Organization-level single sign-on also enables logins to legacy applications without heavy integration projects

Intelligent application profiling significantly speeds up deployment by identifying application login windows and automating the login process. This way, legacy and traditional applications can also be integrated into the organization’s single sign-on quickly, cost-effectively, and reliably, just like all other applications.

Read more

Access management and shared devices bring production security to the manufacturing industry

Cybersecurity must not stop production—and production must not compromise cybersecurity. In the manufacturing industry, every second counts. A production line downtime does not just mean lost time, but often also significant costs, delivery delays, and a decline in customer satisfaction. At the same time, industrial companies face growing cybersecurity threats and tightening compliance requirements.

The operating environment has changed rapidly. Production lines increasingly utilize digital systems, mobile applications, production control, quality management, and real-time reporting. At the same time, employees must be able to access these systems quickly, securely, and without unnecessary interruptions.

Production Reliability Shared Devices

See also…

Read more
Explore the technology Watch a video about shared mobile devices
What is a PAS solution and how does it work

Would you like to ask an expert more about this topic?

Leave us a message, and we will contact you as soon as possible.

Jyri Forsström

Sales

+358 40 537 0232

jyri.forsstrom(at)csit.fi

CTA-Asiantuntijat

An Assessment of your organization’s current state

TAKE A QUICK ASSESSMENT

How well does your organization manage users and access rights?

This short (2–3 min) quick assessment helps identify the current maturity level, key risks, and most important areas for development.

Would you like to know more about our identity and access management solutions?

Leave us a message, and we will contact you as soon as possible.

CTA-Yleinen (#20)

Antamiasi henkilötietoja käytetään yhteydenottopyyntöösi vastaamiseen sekä yrityksemme tuotteiden ja palveluiden markkinointiin siltä osin kuin ne liittyvät työtehtäviisi. Lisätietoja henkilötietojen käsittelystä, oikeuksistasi ja tietojen säilytysajoista löydät tietosuojaselosteestamme.